Review compliance evidence
Open an evidence record, check its supporting artifacts and linked controls, and record the review decision.
Follow an evidence reviewPrepare for SOC 2, ISO 27001 and HIPAA with the platform and our US-based team. Manage evidence, policies and security findings together. Operators request and review artifacts; you provide business context and approve policies. Advisory and implementation work are separately scoped.
Bring your framework requirements and deadline. We'll discuss evidence work, ownership, and the scope of the annual package.
Read the EchoWin case study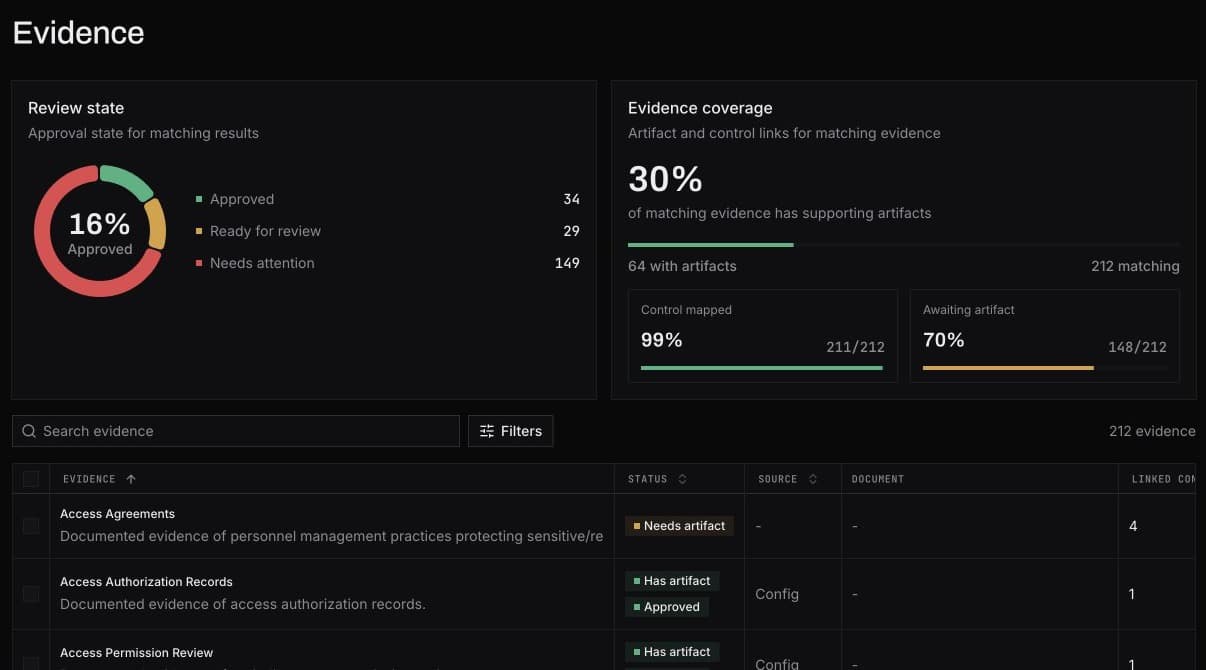
The platform keeps evidence, controls and decisions together. Our own US-based employees handle the agreed security and compliance work alongside your team. We do not outsource or offshore delivery.
See supporting artifacts, linked controls and review status together. Our team helps collect evidence and resolve gaps; designated reviewers decide what to approve.
Review control tests and outstanding evidence throughout the year. Use the platform to see what needs attention before preparing your next audit package.
Completed pentests with published reports link automatically to applicable compliance evidence. New applicable reports update that link, while evidence approval remains a separate review.
We provide existing scoped evidence and correct our deliverables. Audit coordination, auditor meetings, and bespoke questionnaires require a separate scope. The independent assessor determines the outcome.
Agree the scope, connect your systems and prepare evidence for review. We coordinate the work with your team and support the independent assessment.
We agree which frameworks you actually need - SOC 2, ISO 27001, HIPAA - and lock the scope. No paying for controls that will never apply to you.
Integrations pull live config from your cloud, identity, and code. We baseline where you stand today against every control in the chosen frameworks.
Link supporting artifacts to the applicable controls. Published pentest reports can supply evidence from testing completed by our team.
Supported integrations gather artifacts. Review collection status and freshness, and request missing evidence from the people responsible.
Operators review technical evidence and explain gaps. You supply business context and approve policies. Implementation requires separate scope; approval does not prove a control is effective.
We provide existing scoped evidence for independent review. Auditor meetings and coordination are separately scoped; the assessor determines the outcome.
Start with a specific task, then follow the walkthrough to see who acts and what needs review.
Open an evidence record, check its supporting artifacts and linked controls, and record the review decision.
Follow an evidence reviewWhen a pentest is completed and its report is published, the latest applicable report links to eligible compliance evidence. Review and approval remain separate.
See testing and retestingReview findings by source and asset, track remediation deadlines, and check the outcome of scheduled scans.
See scheduled scanning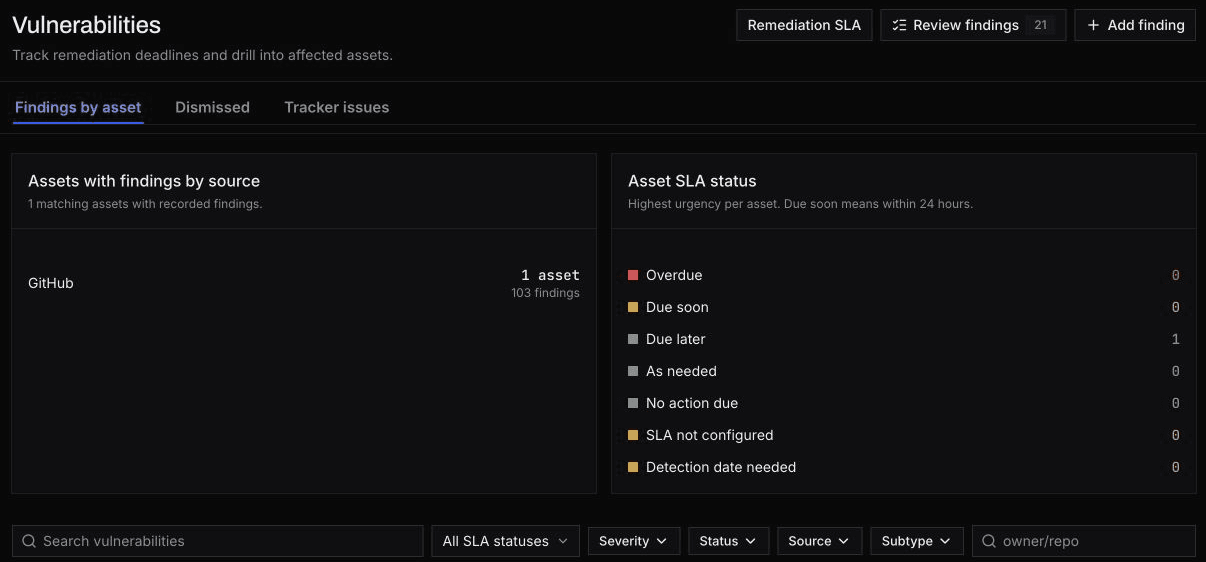
Our published case study covers penetration testing, vulnerability management and compliance support for echowin's AI platform.
Jarred, Andrew, and their team are trusted partners - extensive penetration testing, code analysis, and security reviews that protect our users. We share a vision of prioritizing customer security above all else.
$20,000/year including one framework. Each additional framework is $3,000/year. For companies under $5M revenue or 50 staff. The SOC 2 Type I, Security-only bundle includes the independent auditor fee. Type II audits, additional audit criteria, and other certification fees are quoted separately. Enterprise pricing is custom. The SOC 2 Type I, Security-only bundle is $20,000/year total, including the $3,000 independent auditor fee. Sythe coordinates preparation and the audit through the platform. The independent auditor performs the audit and issues the report. Type II audits and additional criteria are quoted separately.
Each year includes 2 scoped penetration tests, one scoped retest per test, 2 risk assessments, and 12 vulnerability scan runs. Asset and host limits are agreed before work starts. Schedule testing within the service year, subject to availability. Managed security plans have no per-seat platform fees. One compliance framework is included; additional frameworks are annual add-ons. Standalone pentests are priced per engagement; Knell subscriptions use per-user pricing.
Sythe operators request and review evidence, prepare materials, and follow up in the platform. You supply business information and approve your organization's policies. Routine clarification, corrections, and supported platform integration repairs are included.
Ongoing security monitoring and incident response are additional services. We recommend fixes; hands-on changes to your systems require a separate implementation scope.
Strategic compliance advice and expressly delegated decisions use a vCISO retainer at $250/hour, with hours approved in advance. Kickoff and pentest scoping and closure meetings are included. Other routine delivery happens in the platform; recurring consulting meetings are extra.
Bring the customer's request or the audit requirement to a 30-minute scoping call. These details help us work out what belongs in your program. Leave unknowns open; you do not need a finished compliance plan to talk to us.