Managed security
Infinite Outdoors
A four-person team with payment data, no security function, and a Series A closing.
Read the Infinite Outdoors storyManaged SOC 2 for small teams
Bring the request. We’ll help clarify the report they need, the work ahead, and whether managed compliance fits your team. Sythe runs the evidence work and scoped testing in one platform.
30 minutes with Andrew · Bring your deadline and customer request
Platform + people + scoped testing
For companies under $5M revenue or 50 staff. One framework included.
The SOC 2 Type I, Security-only bundle includes the independent auditor fee. Type II audits, additional audit criteria, and other certification fees are quoted separately.
Software only: $499/monthSythe operators request and review evidence, prepare materials, and follow up in the platform. You supply business information and approve your organization's policies. Routine clarification, corrections, and supported platform integration repairs are included.
Each year includes 2 scoped penetration tests, one scoped retest per test, 2 risk assessments, and 12 vulnerability scan runs. Asset and host limits are agreed before work starts. Schedule testing within the service year, subject to availability.
Ongoing security monitoring and incident response are additional services. We recommend fixes; hands-on changes to your systems require a separate implementation scope.
Strategic compliance advice and expressly delegated decisions use a vCISO retainer at $250/hour, with hours approved in advance. Kickoff and pentest scoping and closure meetings are included. Other routine delivery happens in the platform; recurring consulting meetings are extra.
Type II readiness and timing depend on your scope, operating history, and auditor. We confirm the delivery scope before you commit.
See the published scope and results. Each engagement is different; these stories aren’t a guarantee of your audit outcome.
Managed security
A four-person team with payment data, no security function, and a Series A closing.
Read the Infinite Outdoors storyHIPAA · SOC 2
HIPAA attestation held and SOC 2 underway, with the whole department owned by us.
Read the echowin storyA short preview of the workspace, evidence review, and auditor handoff. No email required. Sythe prepares the work; your team provides business records and approves its policies.
Sythe: coordinate evidence requests and follow up. Your team: provide business records and confirm owners.
Start with the work that needs attention. The workspace brings assigned actions, policy reviews, and evidence status together so your team can decide what to address next.
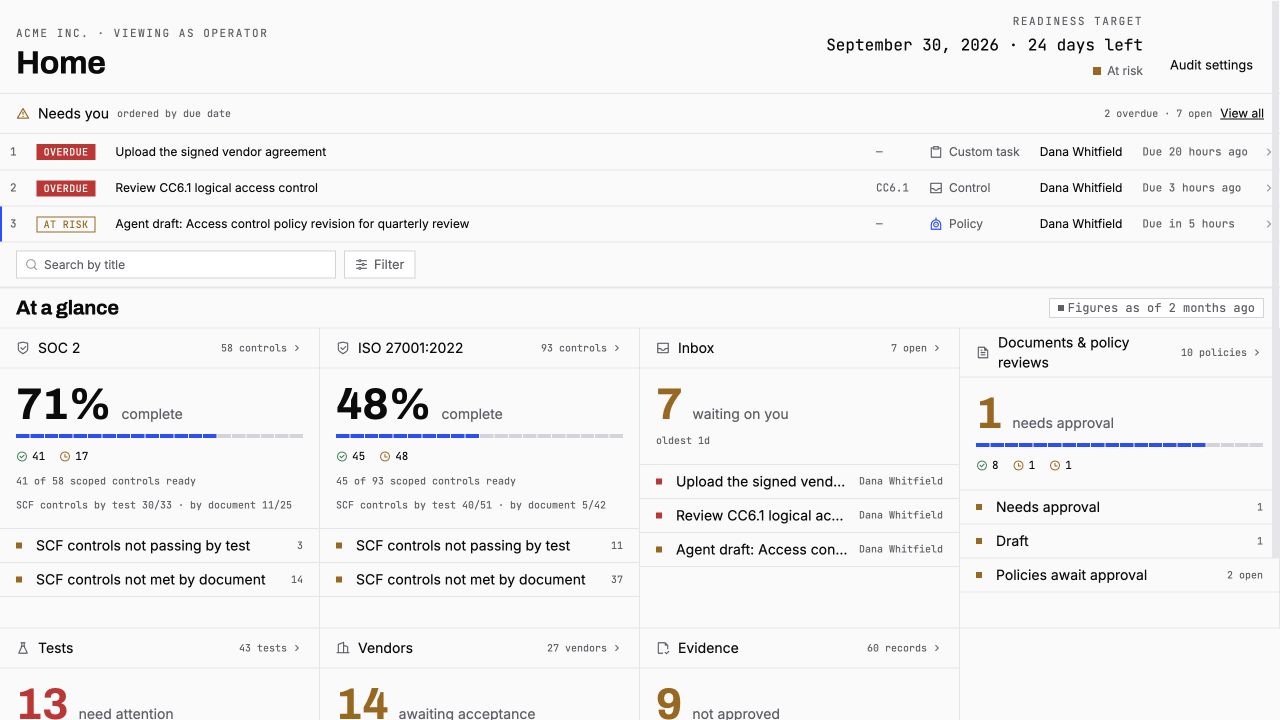
Actual platform components with fictional sample data. Screens show separate examples, including multiple frameworks; the platform plan includes one framework. Click an image to enlarge it.
Book a time now, or send a few details first. Tell us what your buyer requested and when you need it. We’ll confirm fit and the scope to discuss.
Choose a 30-minute call (opens Google Calendar in a new tab)Please summarize the request. Don’t include credentials, confidential reports, or customer evidence.
A Type I is typically achievable in weeks once gaps are closed. A Type II requires an observation window - most companies run three months for a first report and twelve thereafter. The audit firm's fieldwork is a few weeks on top.
No. An independent CPA firm issues the report. We prepare and review scoped evidence. Its fees are separate, as are audit coordination and auditor meetings.
No. The $20,000/year plan includes one framework; SOC 2 can be that framework. Additional frameworks cost $3,000/year each. Routine evidence coordination and preparation are included. The independent audit, auditor meetings, and audit coordination are separate.
Yes. We baseline what exists, keep the evidence that stands up, and tell you plainly which controls were marked ready but would not survive fieldwork.
The criteria do not explicitly mandate a penetration test. Testing can support control evidence, and auditors or customers may request it. Confirm the scope with your auditor; penetration testing is included in the base plan.
Follow the Startup Compliance Atlas steps and prepare the records for review.